The Invisible Door: Common Access Control Mistakes That Make Your Building Vulnerable
Imagine: a resident of an apartment building receives a report of a stolen package in the common hallway. Or an office manager discovers that sensitive documents have been moved, with no camera footage or logs to back them up. Frustrating, isn't it? We often think a sturdy front door with a good lock is sufficient. But in today's world, where every building houses an ecosystem of people, values, and data, the "invisible door"—access control—is just as important as the physical lock.
The reality is that many offices and apartment complexes unknowingly create vulnerabilities in their access control systems. Not intentionally, but due to a lack of understanding of the subtle ways systems can fail, and people—with or without malicious intent—can exploit them. This article will take you on a journey through the most common, yet often overlooked, security flaws in access control. We'll help you understand where the risks lie and how to diagnose your own situation, so you can go from "I hope it's secure" to "I know it's secure."
Access Control 101: More Than Just a Key
Before we dive in, let's lay the groundwork. What exactly is access control?
Simply put, access control is the process of determining:
- Who has access (authentication).
- What they have access to (authorization).
- When they have access (schedules).
- And what they do when they have access (registration).
This goes much further than the old-fashioned key ring. Think of:
- Mechanical systems: The traditional locks and keys.
- Electronic systems: Access passes, codes, intercom systems.
- Biometric systems: Fingerprints, facial recognition.
- Smart systems: Linked systems that are managed via software.
The goal is clear: allow the right people in the right place at the right time, and keep everyone outside of that out. The challenge? It lies in the details and the interaction between technology, policy, and human behavior.
The 7 Deadly Sins of Access Control
Now let's examine the most common vulnerabilities. These are the "deadly sins" that can, without your knowledge, open your building to unwanted guests or situations.
1. Unlimited Key Duplication: The Hidden Copy
Traditional keys offer the convenience of simplicity, but harbor a serious vulnerability: unlimited duplication. When keys aren't protected against unauthorized copying, you lose control over who has a copy, and therefore who has access to your building.
The vulnerability:
Anyone who gets their hands on a key can have it copied relatively easily, unless it's a specially secured cylinder with a certificate. Without this certificate, you have no way of knowing how many keys are in circulation and who owns them.
Example – Apartment complex: A former resident who still has a key or has had a duplicate key made can still enter the complex after moving out. This can lead to theft of mail, packages, or even access to parking garages or storage units.
Example – Office: A disgruntled (ex-)employee duplicates a key and uses it to gain unauthorized access after working hours, for example to commit sabotage, steal data or take property.
The attacker's thought: “With a simple copy I have free access, and no one knows.”
Pitfall! Overestimating the security of "standard" keys. Keys without a unique security certificate are effectively public keys.
Checklist: Do you recognize this error in your system?
- Are all keys issued with a unique, protected certificate?
- Do you know exactly how many keys for each lock are in circulation?
- Are keys collected and recorded when someone leaves?
2. No Log or Audit Trail: The Invisible Doors
Imagine something improper happens. Without a detailed log of who accessed the data, where, and when, it's virtually impossible to reconstruct the event or identify the person responsible.
The vulnerability:
Many traditional and even some electronic systems lack proper access event logging. This means that any access, authorized or unauthorized, goes undetected.
Example – Office: A valuable laptop is stolen from an office space. Several employees and cleaners have access. Without a log of their access times, it's impossible to determine who was present at what time and identify the culprit.
Example – Apartment complex: Vandalism in common areas. Without a record of who opened the doors, the perpetrator remains unknown, and the behavior can be repeated.
The attacker's thought: “Without registration, I can go about my business; no one will be able to trace me.”
Aha moment: A logbook isn't just for tracking, it's also a powerful preventative measure. Knowing that every move is being recorded acts as a deterrent.
Checklist: Do you recognize this error in your system?
- Do your access control systems register all entrances and exits?
- Can you easily view and analyze this data?
- Are these logs regularly checked for abnormal patterns?
3. Lack of Hierarchy & Privilege Escalation: The Free Pass
Not everyone needs the same access. The management has different authorizations than an intern, and the homeowners' association manager has different authorizations than a resident. A flat access structure, where everyone has access to virtually everything, creates enormous risks.
The vulnerability:
When there's no clear hierarchy of access privileges (Role-Based Access Control – RBAC), people are given unnecessary access. This increases the risk of misuse, errors, or sensitive information falling into the wrong hands.
Example – Office: The cleaning crew has a master key that provides access to all offices, including server rooms or safes containing important data. This poses an unnecessarily high risk. An adjustment of the locking plan can provide easier and more secure access.
Example – Apartment complex: A resident has a tag that opens not only the main entrance, but also the utility room, the homeowners' association meeting room, and the elevator to all floors. This violates the principle of "least necessary privileges."
The attacker's thought: “If everyone has access to everything, it won't be noticed if I do it too.”
Checklist: Do you recognize this error in your system?
- Is each user's access tailored to their specific role and function?
- Are access privileges automatically updated when a role changes or I move?
- Are there “master keys” or tags in circulation that give too much access?
4. Poor Physical Integration with the Building: The Back Door
An advanced access control system on the main entrance is useless if a side door is open, a window is unlocked, or the surrounding wall is easily breached. Security is a chain; the weakest link determines its strength.
The vulnerability:
Access control is often considered isolated from the physical integrity of the building. Gaps in fences, weak windows, easily forced doors, or systems that don't integrate seamlessly with alarms and CCTV create "back doors."
Example – Office: A building with electronic access at the front, but an emergency exit at the rear secured only with a simple panic lock and not integrated into the access control system or alarm system. This is an easy entry point for burglars.
Example – Apartment complex: The access door to the storage rooms has a good lock, but the windows of the storage rooms are easy to force and provide access to the space, or the communal gate is often open.
The attacker's thought: “Why should I try the front door when I can easily get in through the side door or a window?”
Checklist: Do you recognize this error in your system?
- Are all possible access points (doors, windows, gates) secured in a consistent manner?
- Does your access control system work with your alarm system and camera surveillance?
- Is the physical integrity of the building regularly checked for weaknesses?
5. Human Error & Lack of Awareness: The Open Door
Technology is powerful, but the human factor remains the greatest vulnerability. Politeness, haste, or simply a lack of awareness can bypass even the most advanced systems.
The vulnerability:
Tailgating is a classic example: someone holds the door open for a stranger out of politeness, without checking if they are authorized. Writing down codes, losing tags, or failing to report an incident are also common human errors. Approximately 80% of security incidents have a human component.
Example – Office: An employee holds the parking garage barrier open for a car driving directly behind him, without knowing whether this is a colleague or an unauthorized person.
Example – Apartment complex: A resident lets in someone claiming to be "the delivery person" through the intercom without further verification. This could be a so-called "social engineering" attempt.
The attacker's thought: “I don’t have to crack the technology; I crack the human.”
Beware! A strong security culture is as important as the technology itself.
Checklist: Do you recognize this error in your system?
- Are residents/employees trained in security awareness (e.g., tailgating, handling codes/tags)?
- Are there clear procedures for reporting lost keys/tags?
- Is there active monitoring of unsafe behavior (e.g. open doors)?
6. Outdated or Unupdated Systems: The Digital Rust
Technology is evolving rapidly, and security risks evolve along with it. A system that was top-notch five years ago could be riddled with known vulnerabilities today if it's not updated regularly.
The vulnerability:
Software in electronic access control systems, like any other software system, requires updates to patch security vulnerabilities and improve functionality. Moreover, outdated hardware is easier to compromise with modern hacking techniques.
Example – Office: An old, standalone access control system with a known firmware vulnerability. A hacker with the necessary expertise could gain undetected access to the network or physical spaces. This could even lead to ransomware attacks that paralyze entire business operations.
Example – Apartment complex: Old intercom systems or electric locks that are easy to manipulate with standard tools, because they no longer meet current security standards (such as SKG 3-star for cylinders).
The attacker's thought: “Why should I make a fuss when there is an old system in place that I can exploit online?”
Checklist: Do you recognize this error in your system?
- When was your access control system last updated or overhauled?
- Are security patches from the vendor installed in a timely manner?
- Do the physical cylinders in your doors still have a recent SKG quality mark?
7. Overreliance on One Technology: The One-Sided Approach
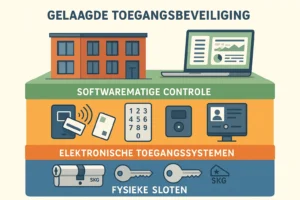
It's tempting to think that a single smart technology—an app, a biometric scanner—is the ultimate solution. But overreliance on a single layer of security, without a layered approach, creates a single point of failure.
The vulnerability:
If one technology fails (power outage, network issue, software bug) or is bypassed, the entire security system collapses. A robust system combines multiple, independent layers of security.
Example – Office: An office that relies entirely on fingerprint scanners for access. What if the scanner fails, or the system crashes? Without a reliable backup (e.g., physical emergency keys, PIN code), no one can enter or exit.
Example – Apartment complex: A "smart home" with smart locks that can only be controlled via an app. If the Wi-Fi goes down or the app malfunctions, residents can no longer enter or secure their home. Sharing digital keys through vulnerable passwords or apps can also grant unintended access.
The attacker's thought: “If I can bypass that one technology, the whole fortress is open.”
Checklist: Do you recognize this error in your system?
- Is there a layered security with both physical and electronic components?
- Are there reliable backup systems in place if the primary technology fails?
- When choosing a system, is the reliability of all components considered, not just one?
A Robust Locking Plan: From Problem to Professional Solution
Now that you know the common mistakes, it's time to look at the solution: a robust and professional locking planThis goes beyond just good locks; it's a strategy that combines technology, policy, and awareness.
Proactive Prevention: Security by Design
- Layered Defense: Combine physical security (e.g. SKG 3-star cylinders) with electronic systems and procedures.
- Risk assessment: Conduct a thorough analysis of all entry points and potential threats, both external and internal.
- Future-proof: Choose systems that are scalable, flexible and easy to update.
Recovery Strategies: Fixing the Mistakes
- Digital Key Management: Use electronic systems to manage access passes so that you can revoke or change access instantly, and duplication becomes impossible.
- Robust Logging & Reporting: Have systems in place to record every access and generate reports for analysis.
- Role-Based Access Control (RBAC): Define clear roles and grant only the strictly necessary access.
- Multi-factor Authentication (MFA): For extra sensitive areas, combine something you know (code), something you have (pass), and/or something you are (biometrics).
The Crucial Human Factor
- Awareness campaignsInform employees and residents about the risks and the importance of security protocols.
- Clear PolicyFormulate clear rules for issuing keys, handling access passes and behaviour at doors.
- Regular Training: Repeat training and refresh knowledge as threats and technologies evolve.
Legal and Ethical Considerations (GDPR)
Access control, especially with logs or biometrics, falls under privacy legislation (GDPR).
- Purpose binding: Collect only the data that is strictly necessary for the purpose (security).
- Transparency: Inform employees/residents clearly about what data is collected and why.
- Security: Ensure adequate security of the stored personal data.
- Retention periods: Use realistic retention periods for logs.
Your Way to Optimally Secured Access Control
Identifying vulnerabilities is the first step toward a safer building. The next step is action. Use this "Master Checklist" to evaluate your current situation:
Master Checklist: Security Access Control
- Key management: Do I have full control over all keys in circulation and are they protected against unauthorized duplication (e.g. via certificate)?
- Registration: Do my systems record who had access, where and when, and can I easily view this data?
- Hierarchy: Is each user's access strictly tailored to their role/function, and no more than necessary?
- Physical Integration: Are all access points (not just the main door) secured and integrated into the overall security plan?
- CreatingAre employees/residents aware of security risks and trained to demonstrate safe behavior?
- Current Affairs: Is my access control system up to date (both hardware and software)?
- Layered Security: Am I not relying on just one technology, but do I have a layered security strategy?
- Privacy: Do my systems and procedures comply with GDPR guidelines?
If you're unsure about any of these questions, it's time to dig deeper.
Next Steps for Deeper Security
The path to optimal security may seem complex, but you don't have to do it alone.
- Consult a professional: Consider an independent audit of your current system by a security expert.
- Invest in quality: Choose proven, certified products that meet the highest standards, such as SKG 3-star cylinders.
- Stay alert: Security is not a one-time task, but an ongoing process of monitoring, updates and awareness.
By investing in a robust locking plan and taking a proactive approach, you transform the “invisible door” from a vulnerability into a powerful shield for your office or apartment complex.
Frequently Asked Questions about Access Control and Security
Q1: What is the difference between a standard lock and an SKG 3-star cylinder?
A1: A standard lock offers basic security. An SKG 3-star cylinder is independently tested and certified to withstand various burglary methods such as core pulling, drilling, and picking for at least 5 minutes. This means significantly higher burglary resistance and greater peace of mind.
Q2: What is “tailgating” and how do I prevent it?
A2: Tailgating (or following) is when an unauthorized person gains access simply by walking or driving behind an authorized person, for example, when the door is held open out of politeness. Prevention can be achieved by raising awareness, implementing clear rules (e.g., "each person validates their own access"), and possibly by using physical measures such as turnstiles or lock gates.
Q3: I have an old access control system. Do I need to replace it completely, or can I upgrade it?
A3: This depends on the age and nature of the system. Sometimes, a software upgrade or the replacement of certain components is sufficient. In other cases, especially with very outdated systems, a complete replacement is safer and more cost-effective in the long run. A security consultant can assess this for you.
Q4: Are electronic systems always more secure than mechanical locks?
A4: Not necessarily. Security depends on the implementation, management, and quality of the system. Electronic systems often offer more functionality (logs, schedules) and flexibility (remote management), but also require attention to cybersecurity and power supply. Mechanical locks, provided they are SKG-approved and have certificate security, remain a very strong foundation for physical security.
Q5: How can I request a locking plan for my building?
A5: A professional locking plan is tailored to your specific situation and needs. You can contact companies specializing in access control and security solutions. They can advise you on the best approach, from mechanical cylinders to integrated electronic systems, and prepare a detailed proposal.